As medical devices become more interconnected, protecting them against evolving cyber threats has become a core engineering requirement. Traditional, siloed risk management falls short when vulnerabilities can lead to critical failures.
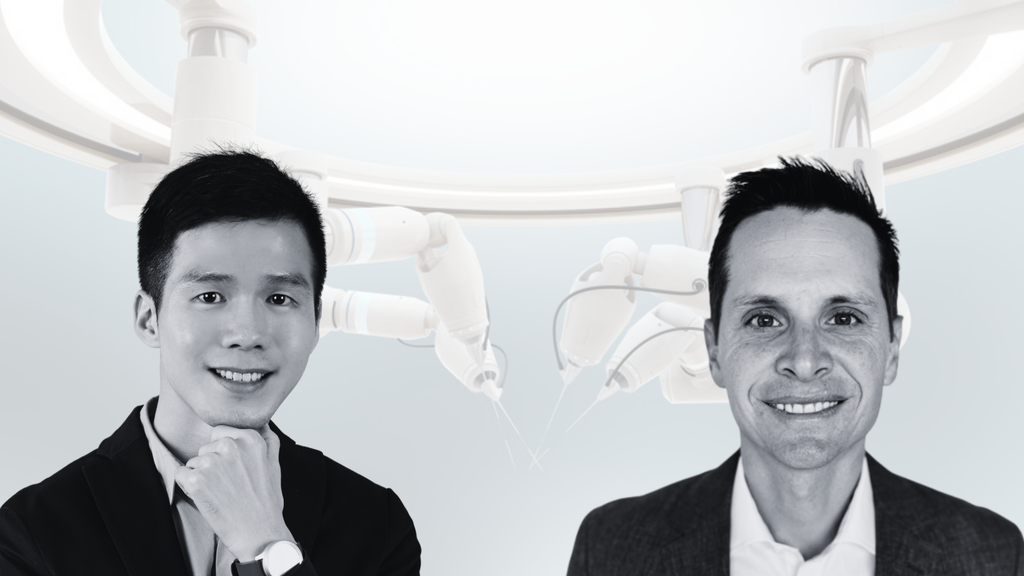
Join Allen Chen, Software Quality Manager at Rook Quality Systems, and Tom Rish, Head of GTM Strategy for MedTech and Life Sciences at Jama Software, for a practical discussion on embedding cybersecurity risk assessment into your development process. Explore how to establish continuous threat modeling, identify vulnerabilities early, and map security requirements directly to system architectures.
What you’ll learn:
- Shift-left security: Identify, assess, and mitigate cybersecurity risks at the requirements stage, before they become costly problems.
- Create Live Traceability: Connect threat models, cybersecurity requirements, and test cases in Jama Connect to maintain a single source of truth.
- Streamline audits & regulatory compliance: Learn best practices for satisfying
FDA cybersecurity guidelines and FDA QSR through automated documentation, post-market surveillance mapping, and live impact analysis.